Security Across Every Connection.
Cybersecurity
How connected products and digital services address access, remote operations, software dependencies, vulnerabilities, and security incidents.
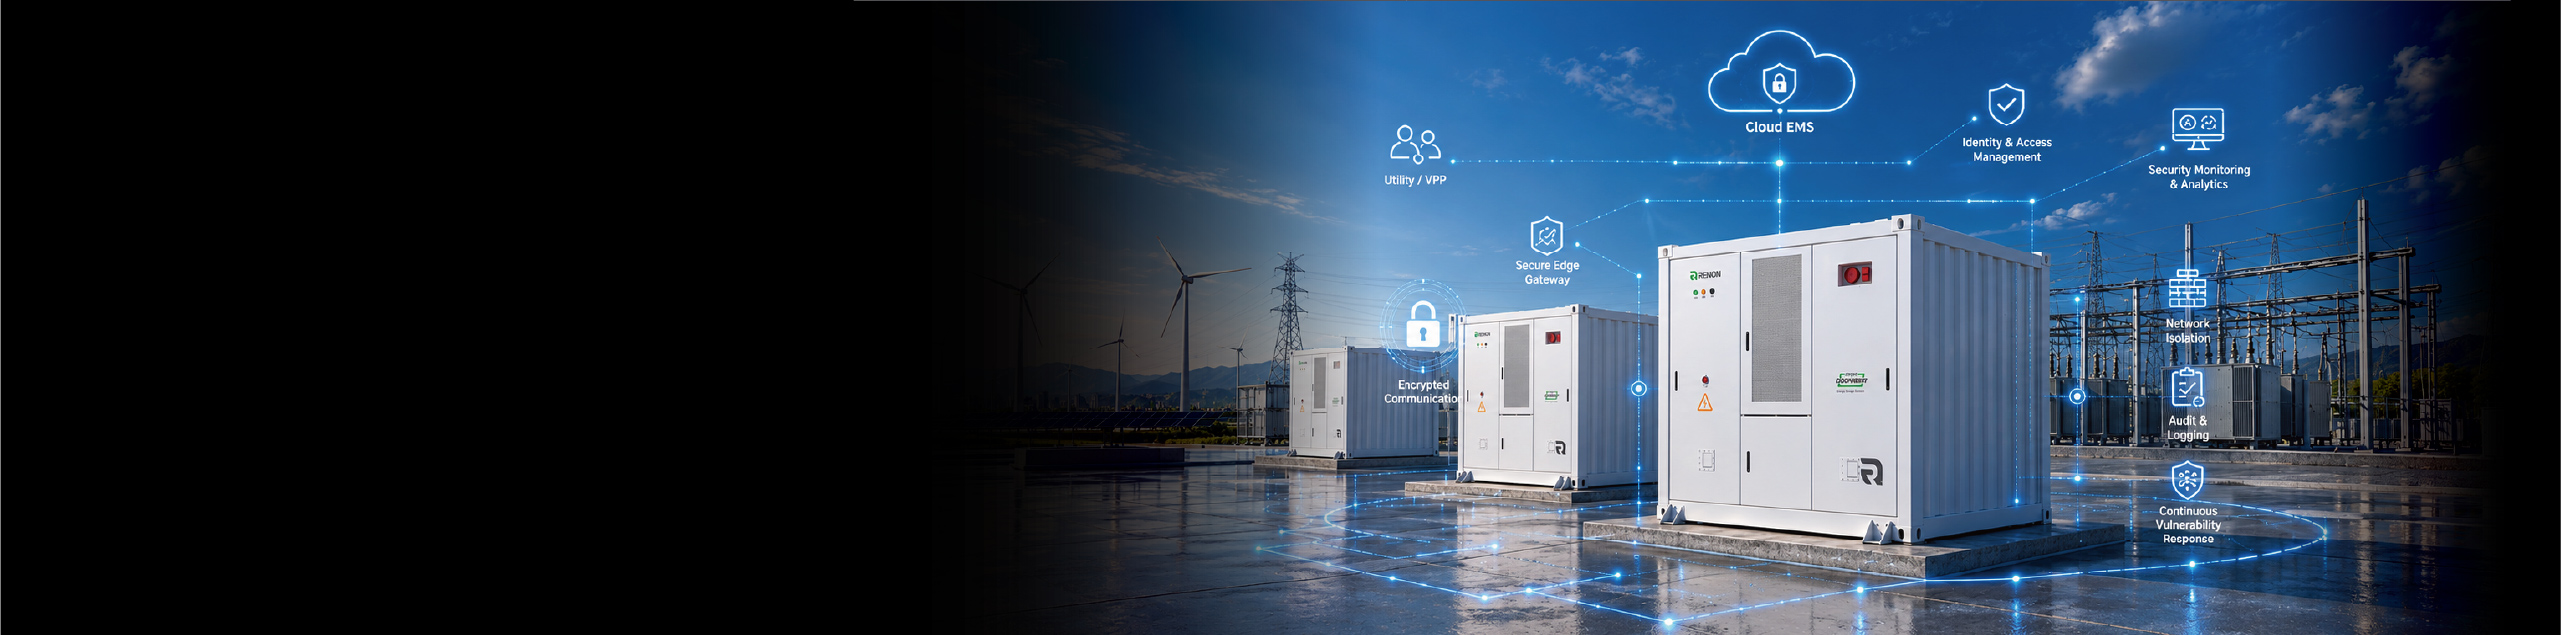
Security Across Every Connection.
Cybersecurity

How connected products and digital services address access, remote operations, software dependencies, vulnerabilities, and security incidents.

Access Control · Secure Development · Vulnerability Management

Cybersecurity
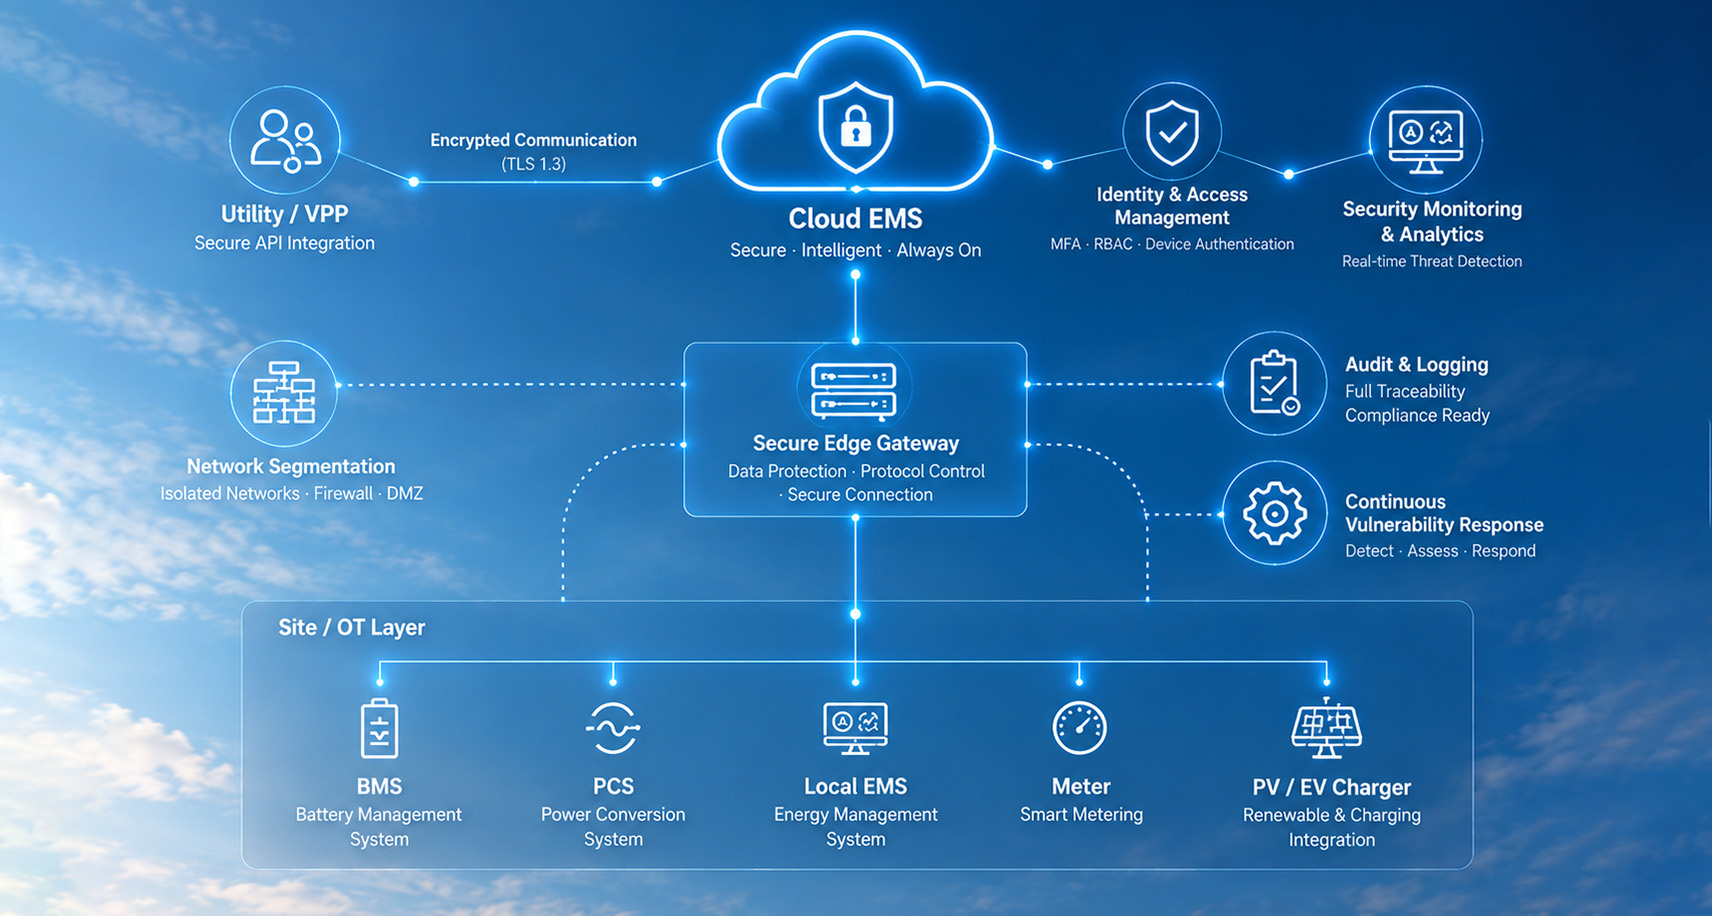
Comprehensive Defense-in-Depth Architecture
Layered protection from system to cell for maximum safety and reliability.
Secure SDLC
RBAC & Auth
Cert & TLS
SBOM Inventory
CVE & Patching
Audit Logging
Incident Resp.
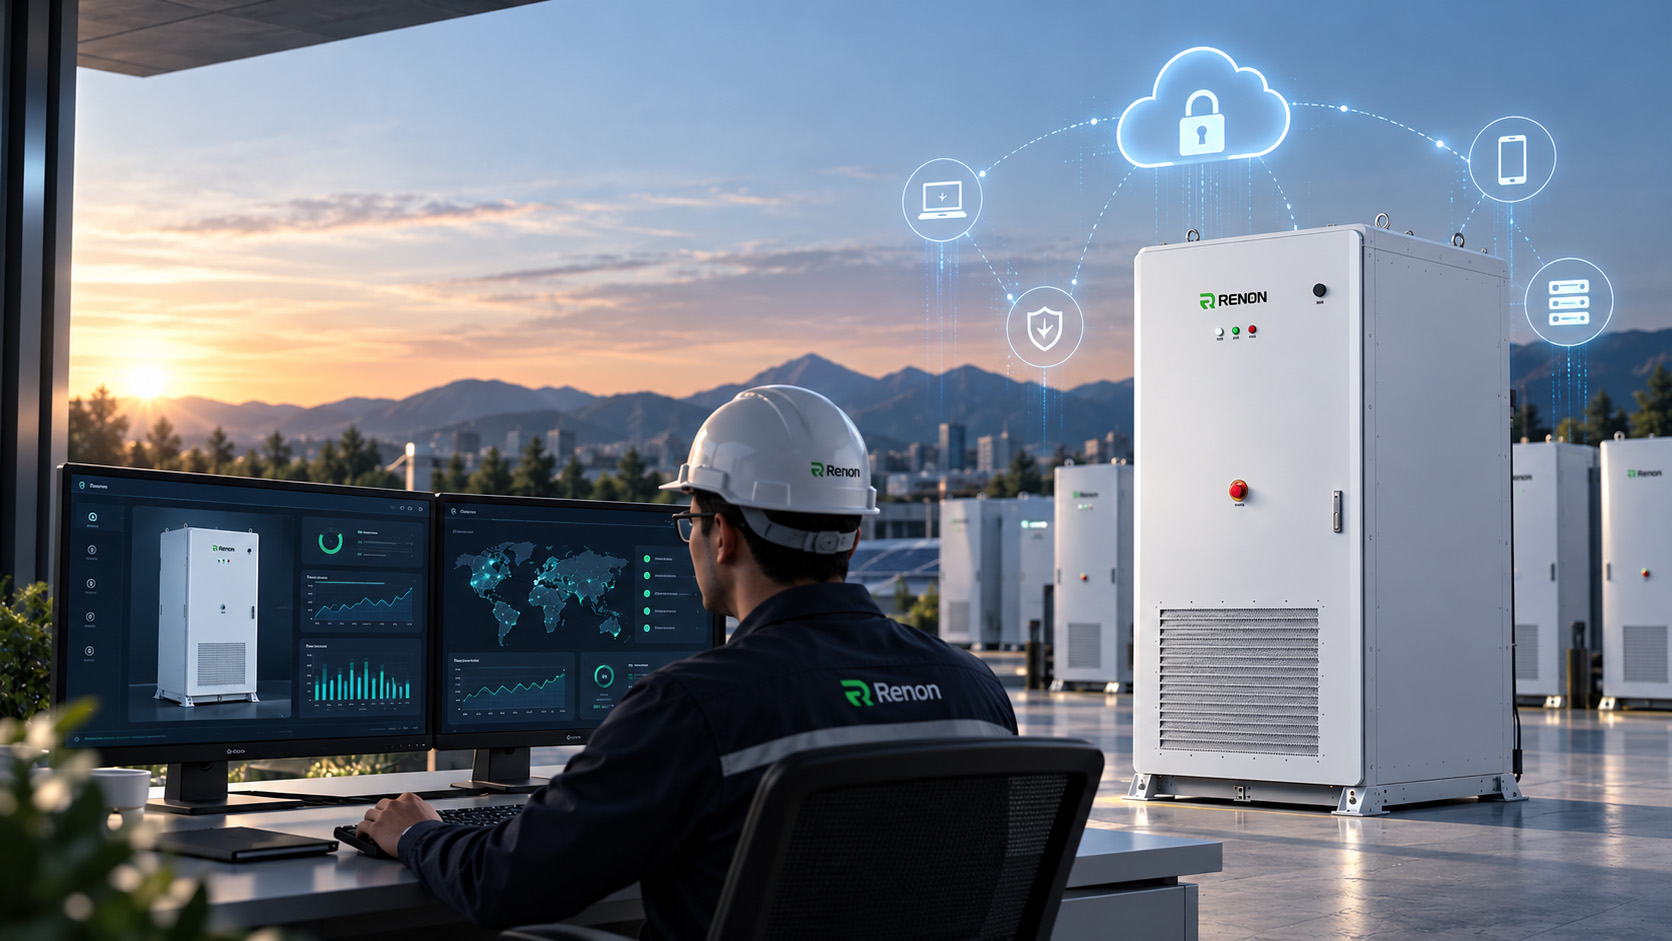
Protecting connected products, software, cloud services, and remote operations.
Cybersecurity is managed across product design, development, access, communication, software maintenance, vulnerability management, and incident response.
Security Governance & Secure Development
For connected products and digital services, appropriate security activities can extend from requirements and architecture through development, testing, release, maintenance, and end-of-life.
Identity, Access & Remote Operations
Users, installers, service personnel, and administrators receive clearly segregated access permissions according to their operational roles. Remote diagnostic and maintenance access is strictly managed according to the applicable product and service security architecture.
Communications & Software Supply Chain
Important communications, credentials, cryptographic certificates, APIs, and other sensitive parameters are managed according to applicable risk profiles. For supported products, software dependencies are systematically tracked through comprehensive component inventories or SBOMs (Software Bill of Materials).
Vulnerabilities, Updates & Security Validation
Potential vulnerabilities are identified through internal testing, third-party intelligence, customer reports, security researchers, or known CVE tracking. Software and firmware updates are managed with rigorous consideration for version control, compatibility, cryptographic integrity, and release governance.
Logging & Incident Response
Relevant login activity, permission changes, remote operations, system abnormalities, and security events are logged where applicable. Security incidents are handled through a defined multi-step process: identification, containment, investigation, remediation, recovery, and appropriate communication.
Protected at Every Layer. Resilient Across Every Connection.
Dedicated technical documentation, SBOM attestation, and coordinated vulnerability disclosure channels for IT, OT, and enterprise security review.
Share